
Pentest reporting platform
AXIOM
Findings in. Reports out.
Create findings, generate PDF reports, and collaborate in real time — one workspace for the whole engagement.
- Scoring
- CVSS 3.1 + 4.0
- Output
- PDF via WeasyPrint
- Editing
- Live, conflict-free
- Import
- Burp · Nessus · Nmap · ZAP
- Self-hosted Runs entirely on your own infrastructure. No engagement data leaves it.
- Encrypted at rest Uploads and secrets sealed with AES-256-GCM.
- Hardened access TOTP, FIDO2, and backup codes on every operator account.
Engagement pipeline
-
Import
Pull scanner output into findings.
-
Author
Write from structured templates.
-
Score
Rate severity with built-in CVSS.
-
Review
Comment and co-edit live.
-
Deliver
Export a client-ready PDF.
Product tour
Follow an assessment from secure access and reusable project types through findings, collaboration, and client-ready reports.

Secure operator access
A focused entry point for teams, with local credentials and single sign-on support.
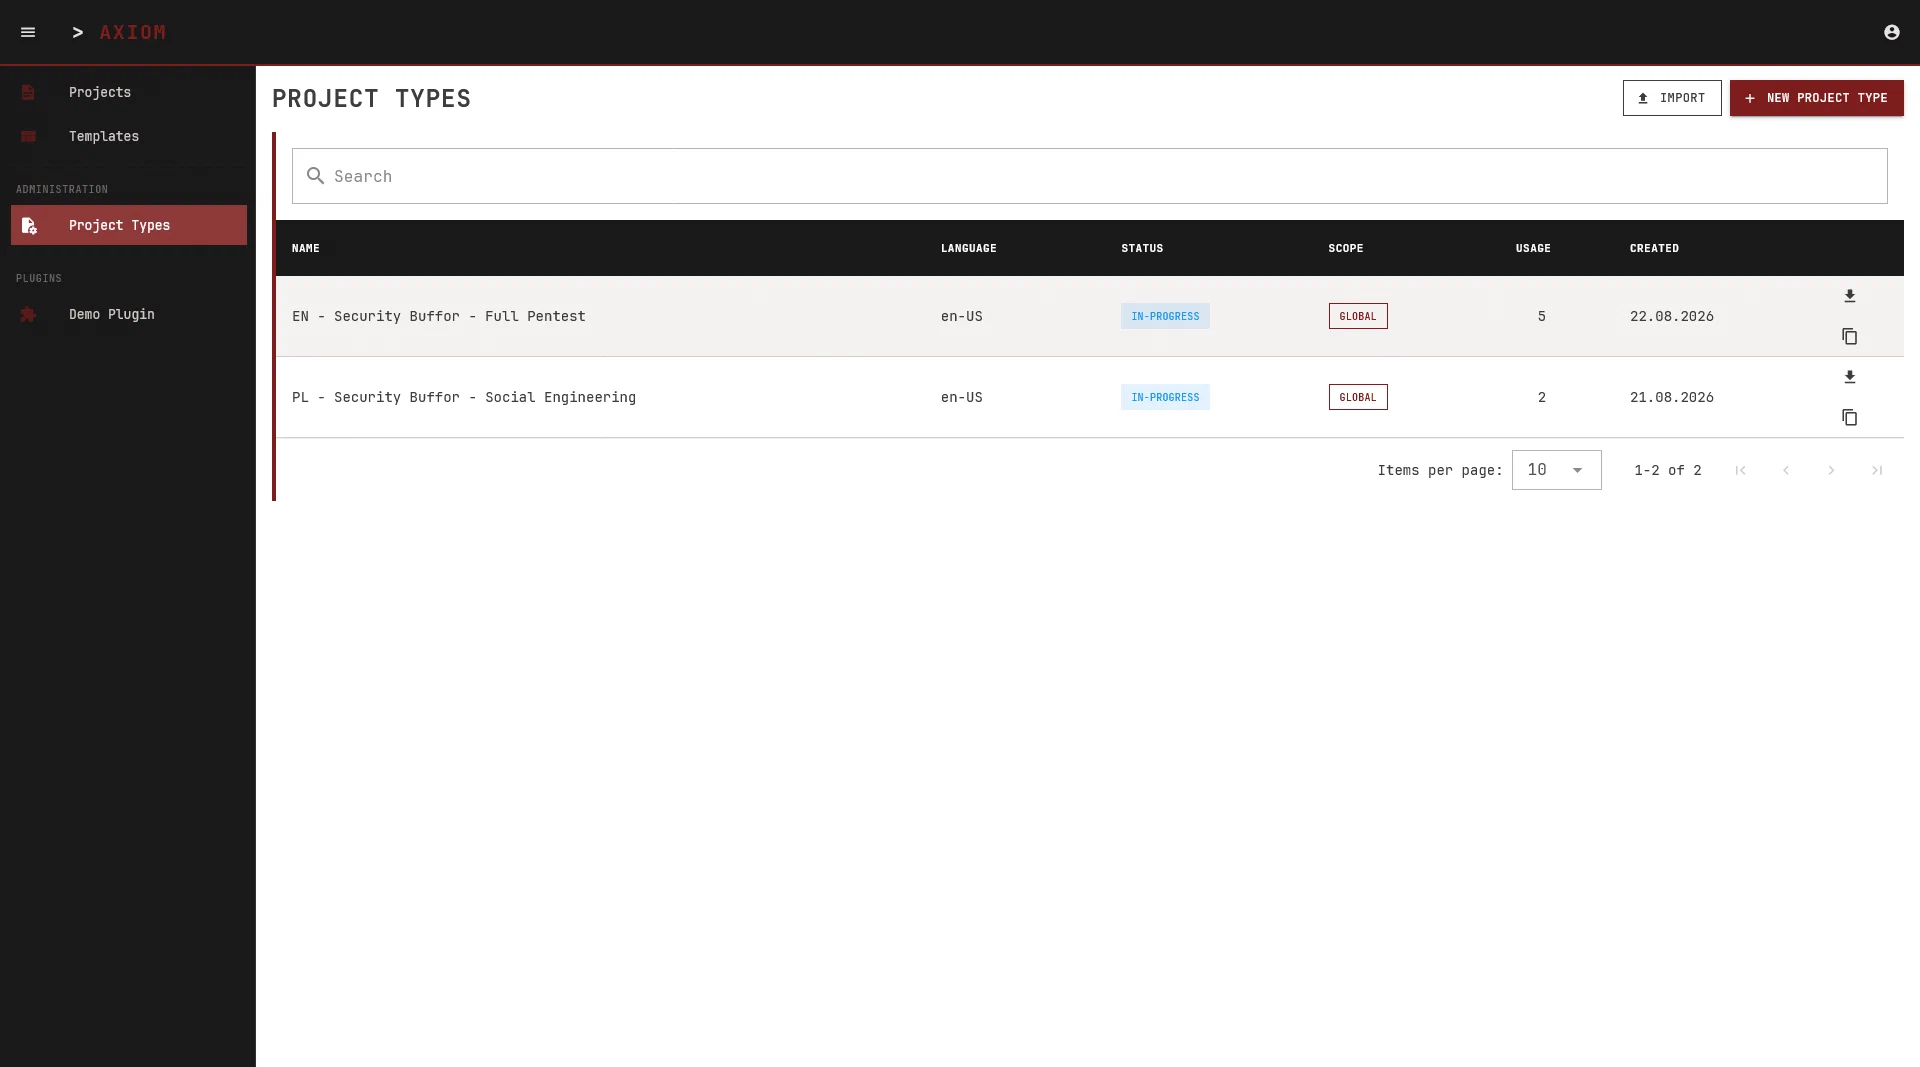
Reusable assessment profiles
Define repeatable project structures once, then apply them across assessments.
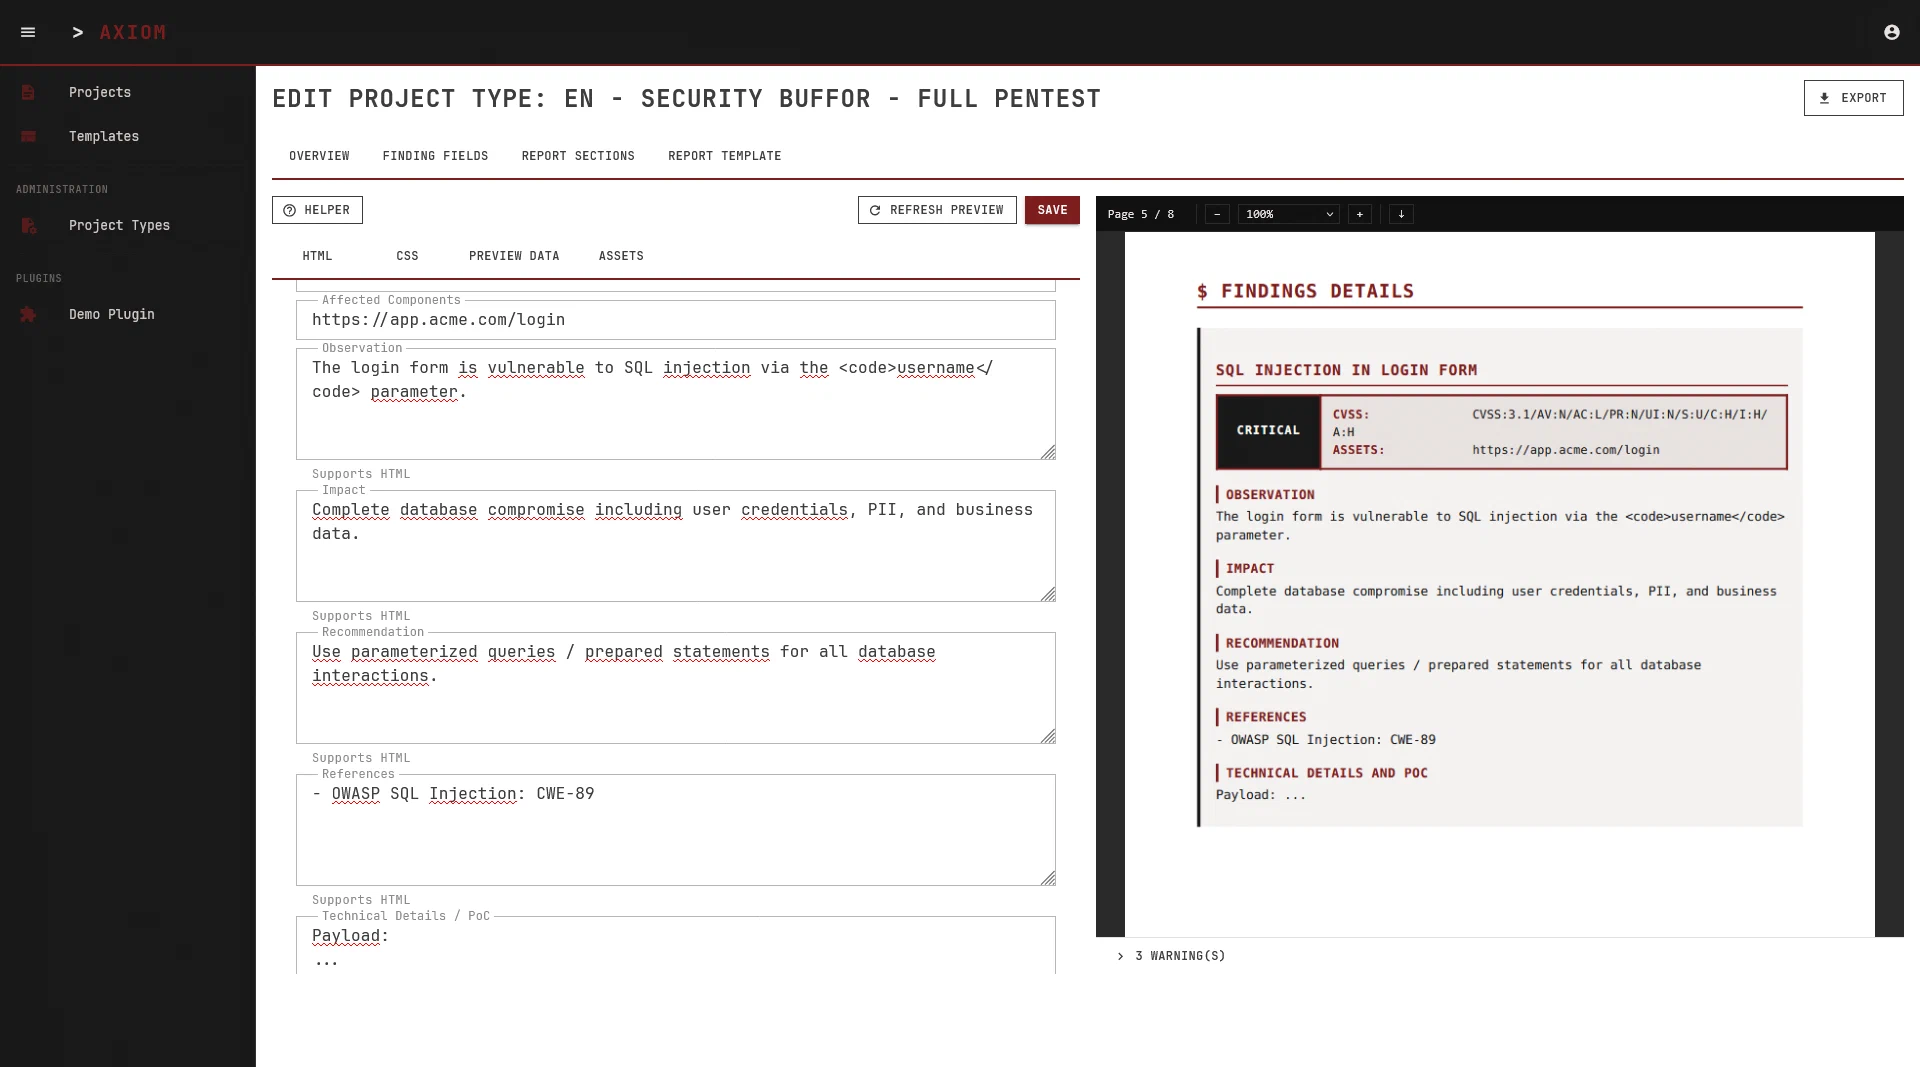
Live report design
Shape report layouts and finding fields while watching the rendered document update.
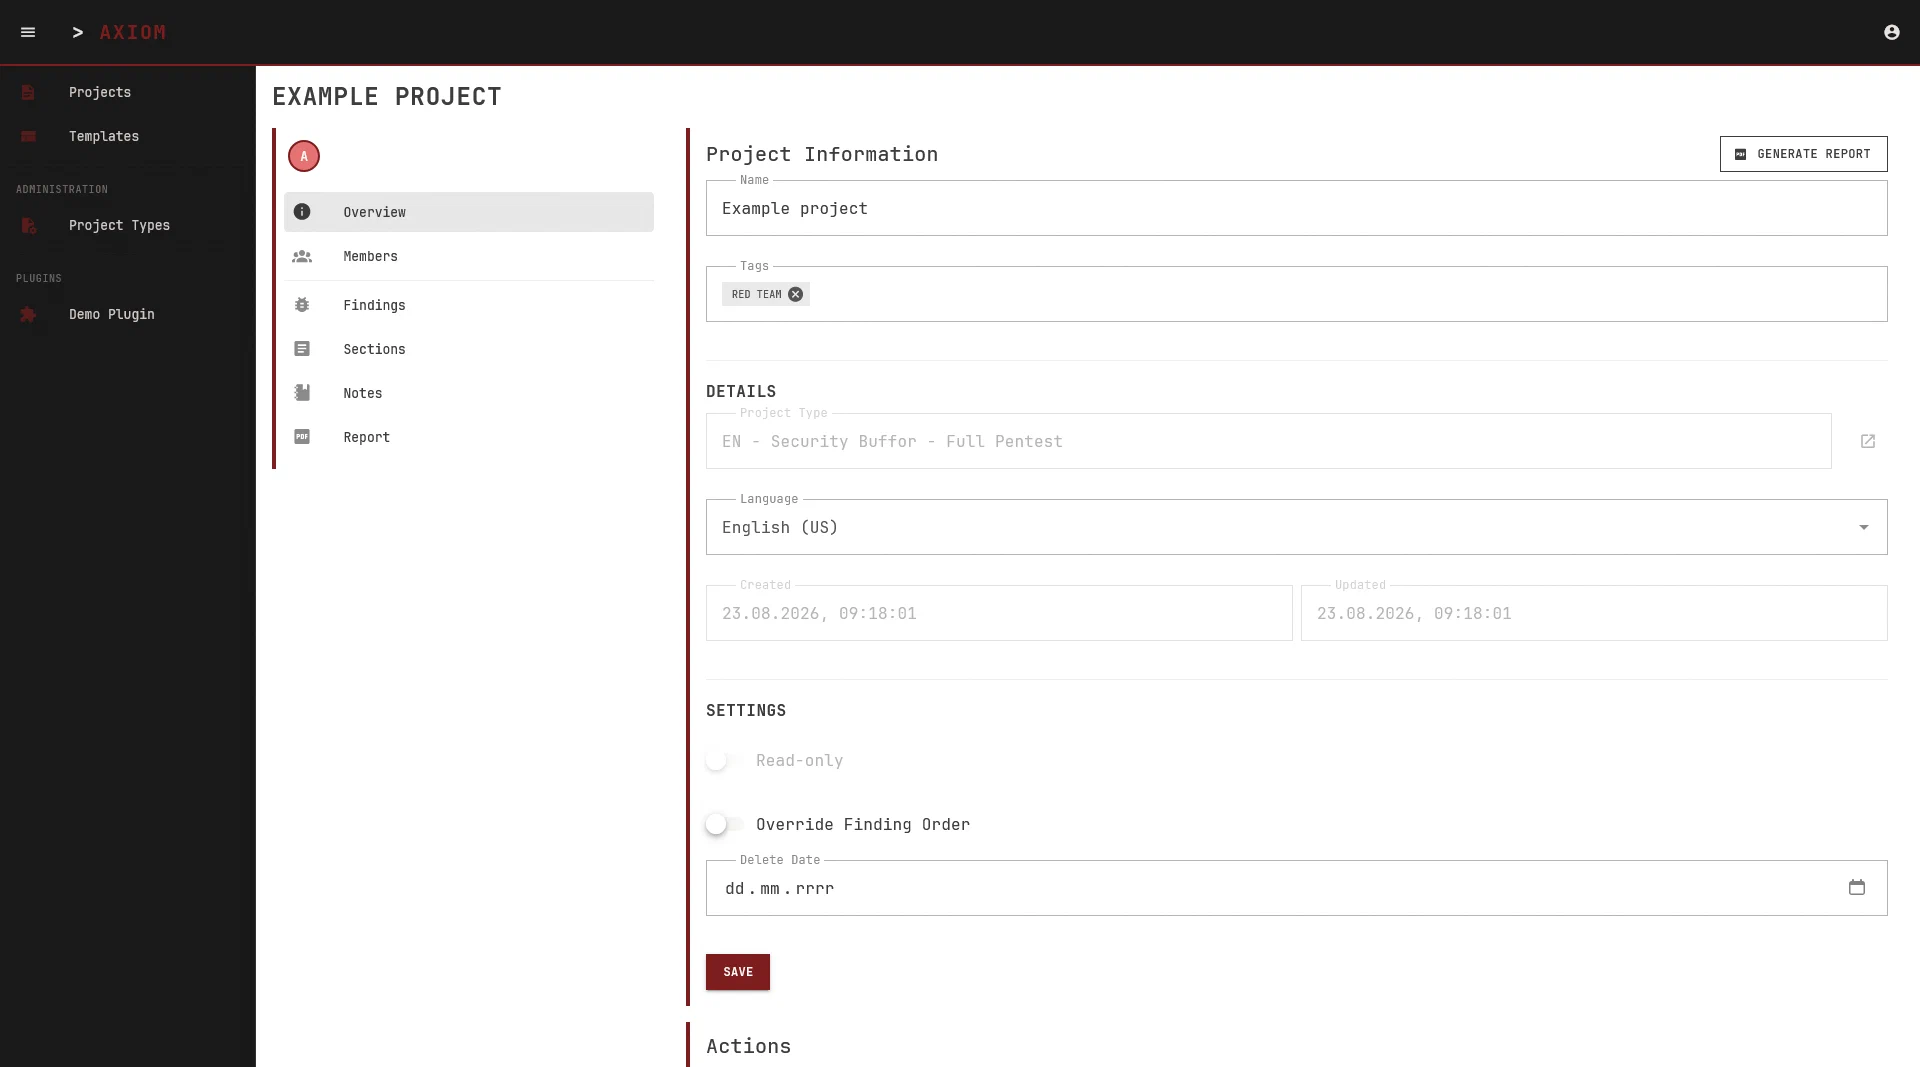
One project workspace
Keep findings, scope, team activity, notes, and deliverables in one operational view.
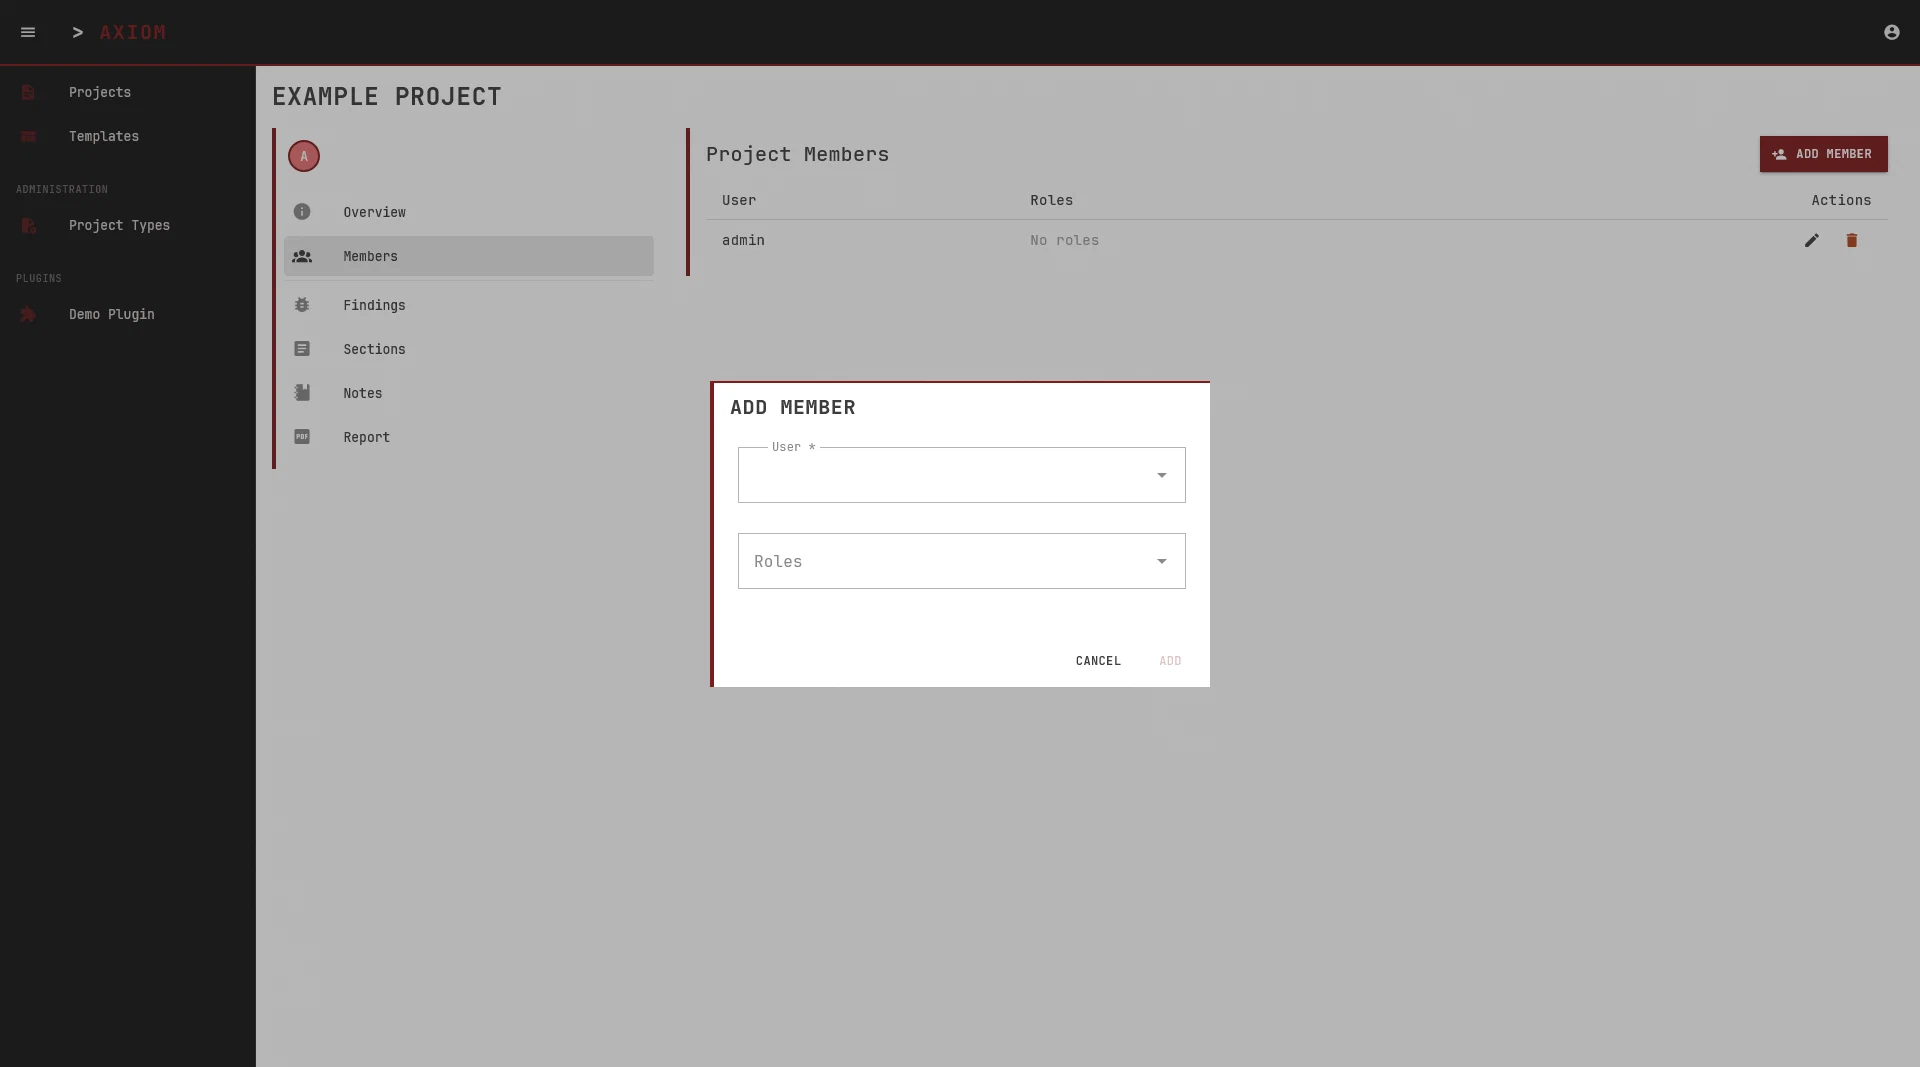
Role-based collaboration
Bring teammates into an engagement with explicit roles and clear access boundaries.
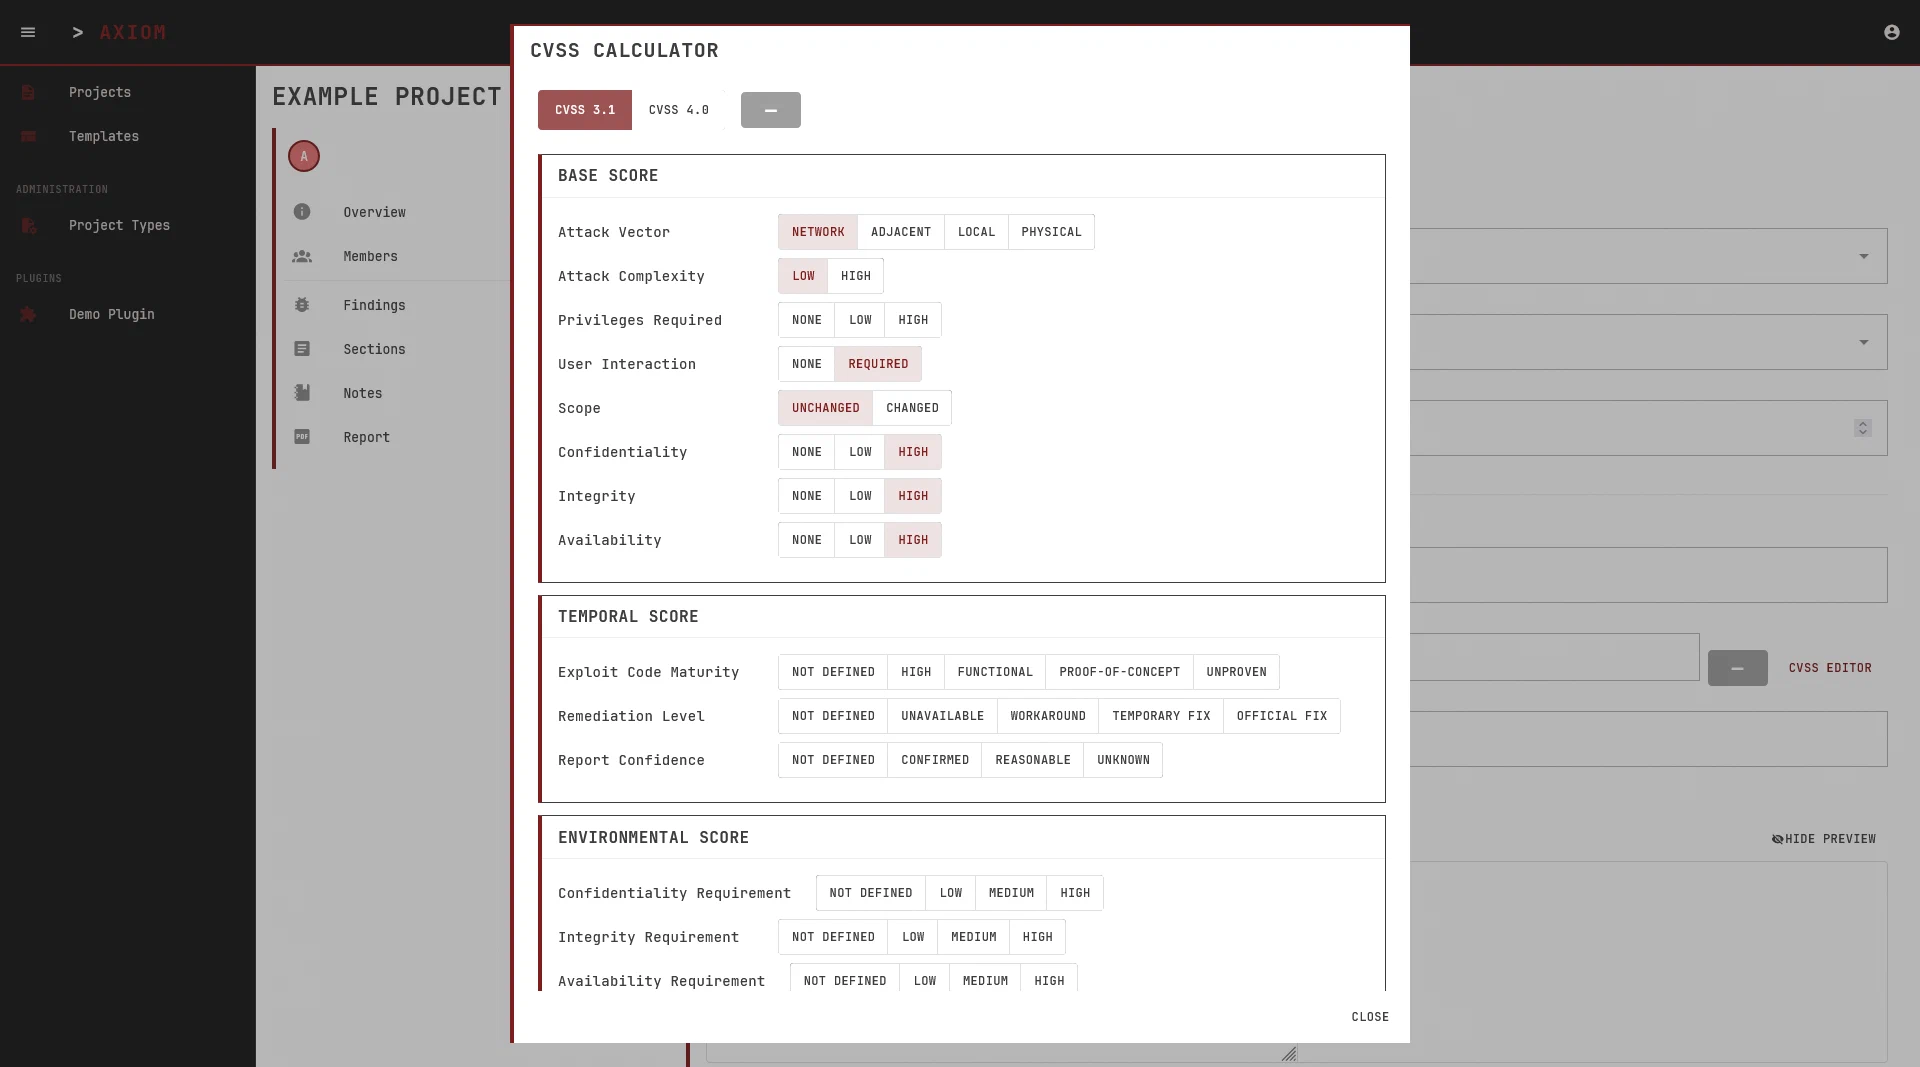
Integrated CVSS scoring
Calculate severity inside the finding workflow without breaking concentration.
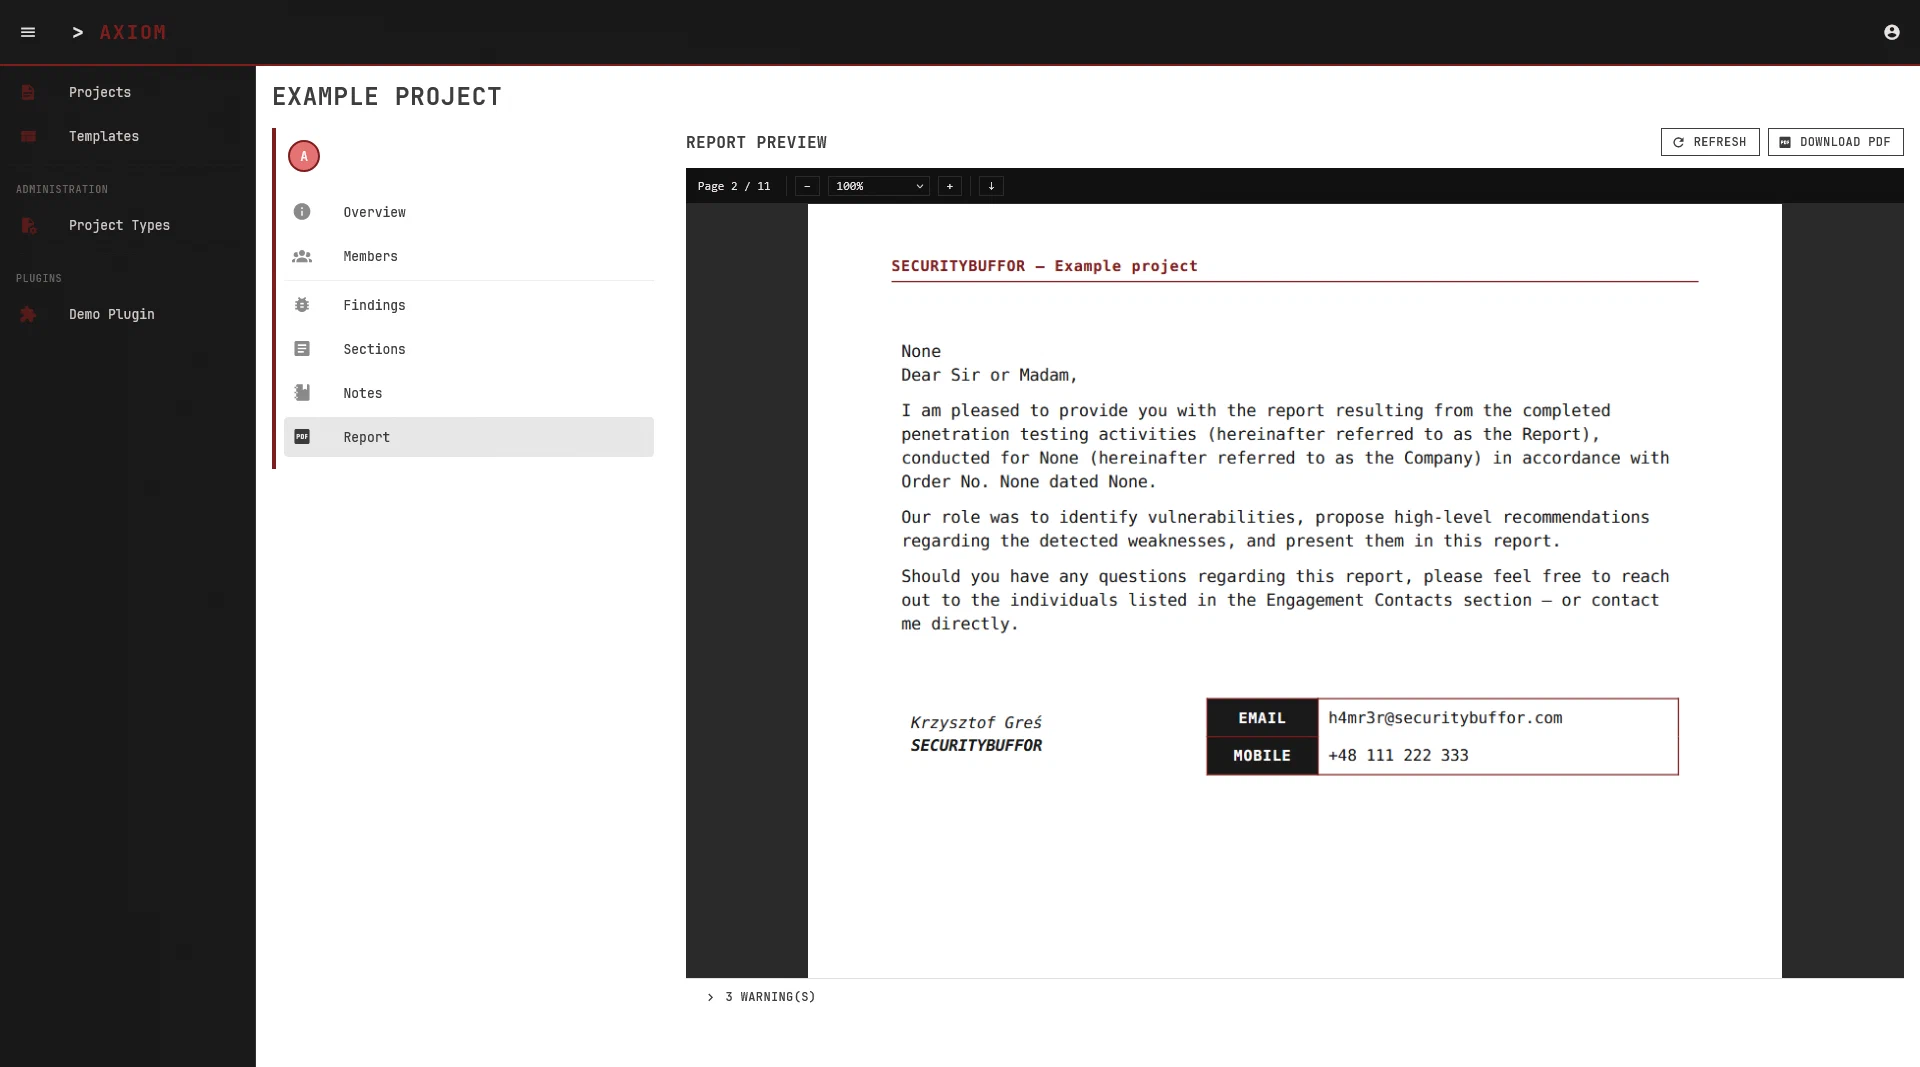
PDF report preview
Inspect the client-ready result before exporting the final assessment report.
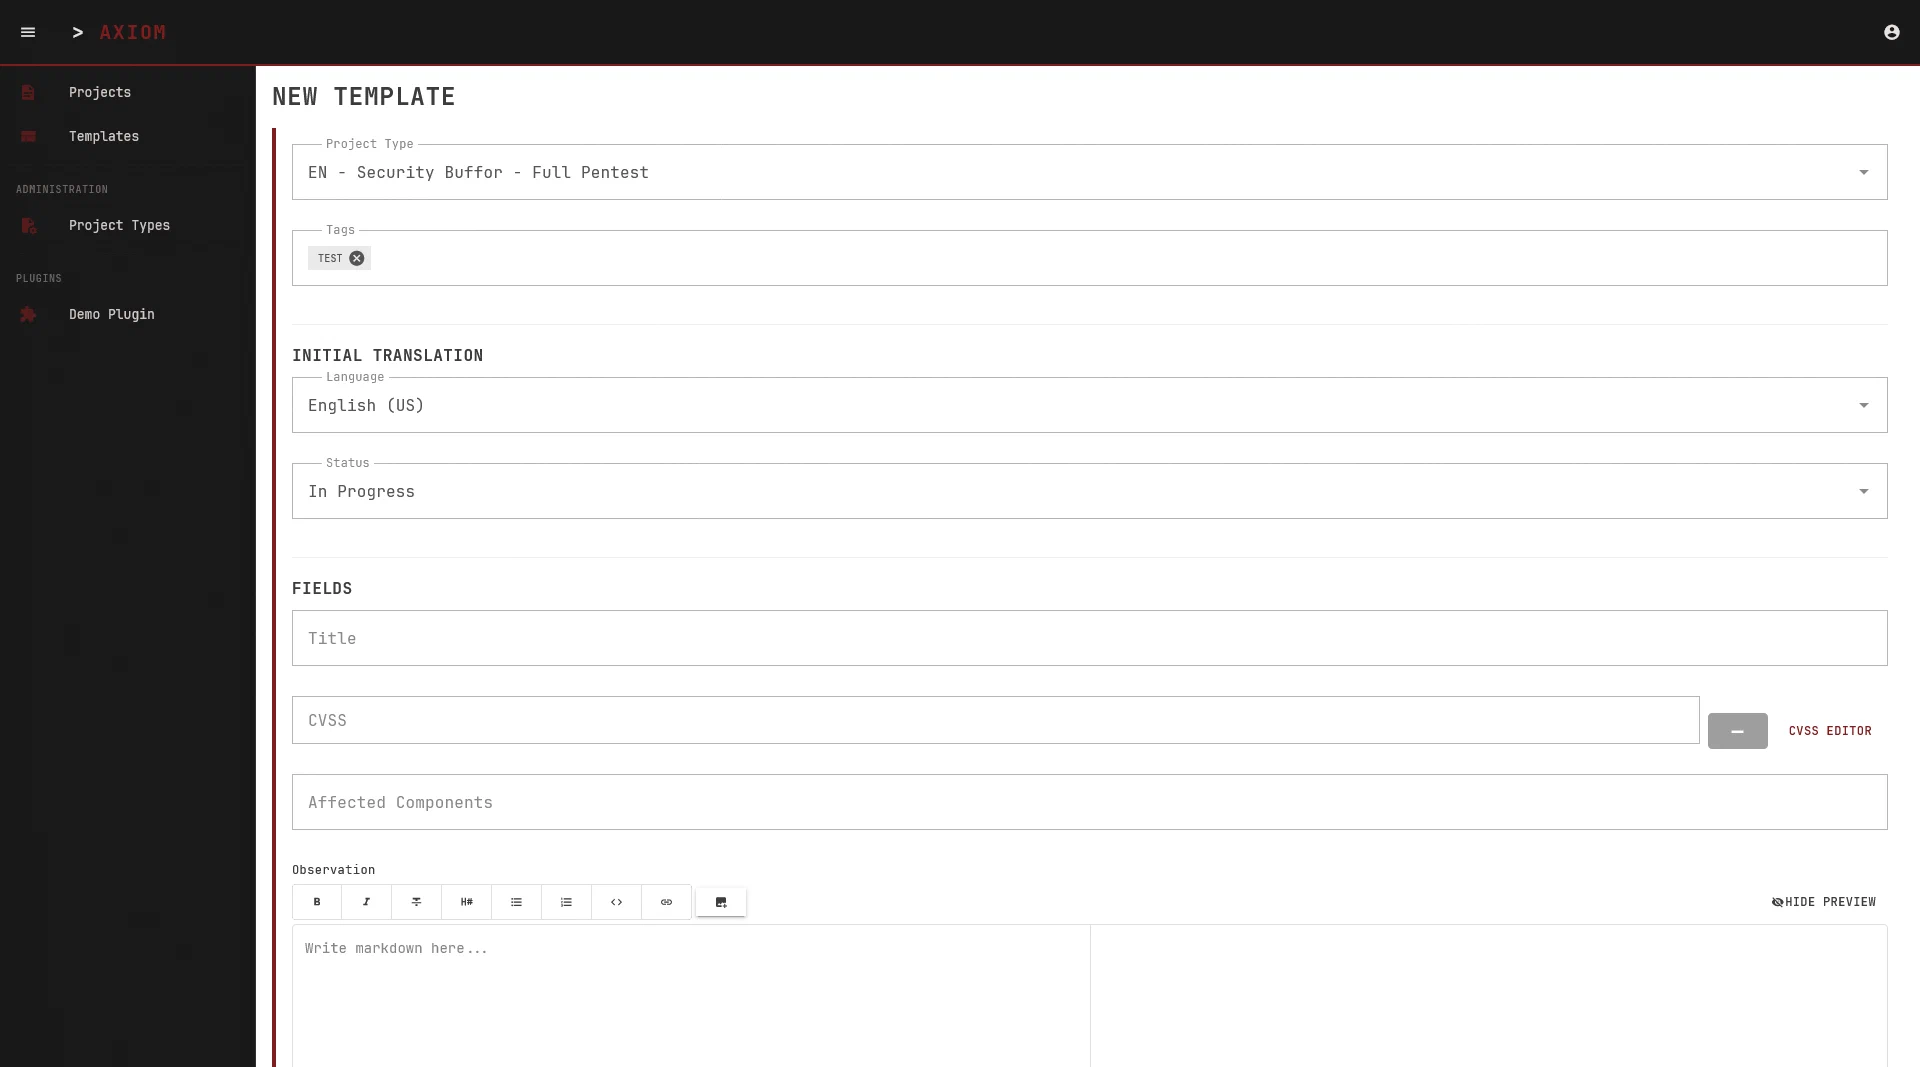
Structured finding authoring
Build consistent findings from reusable, richly structured templates.
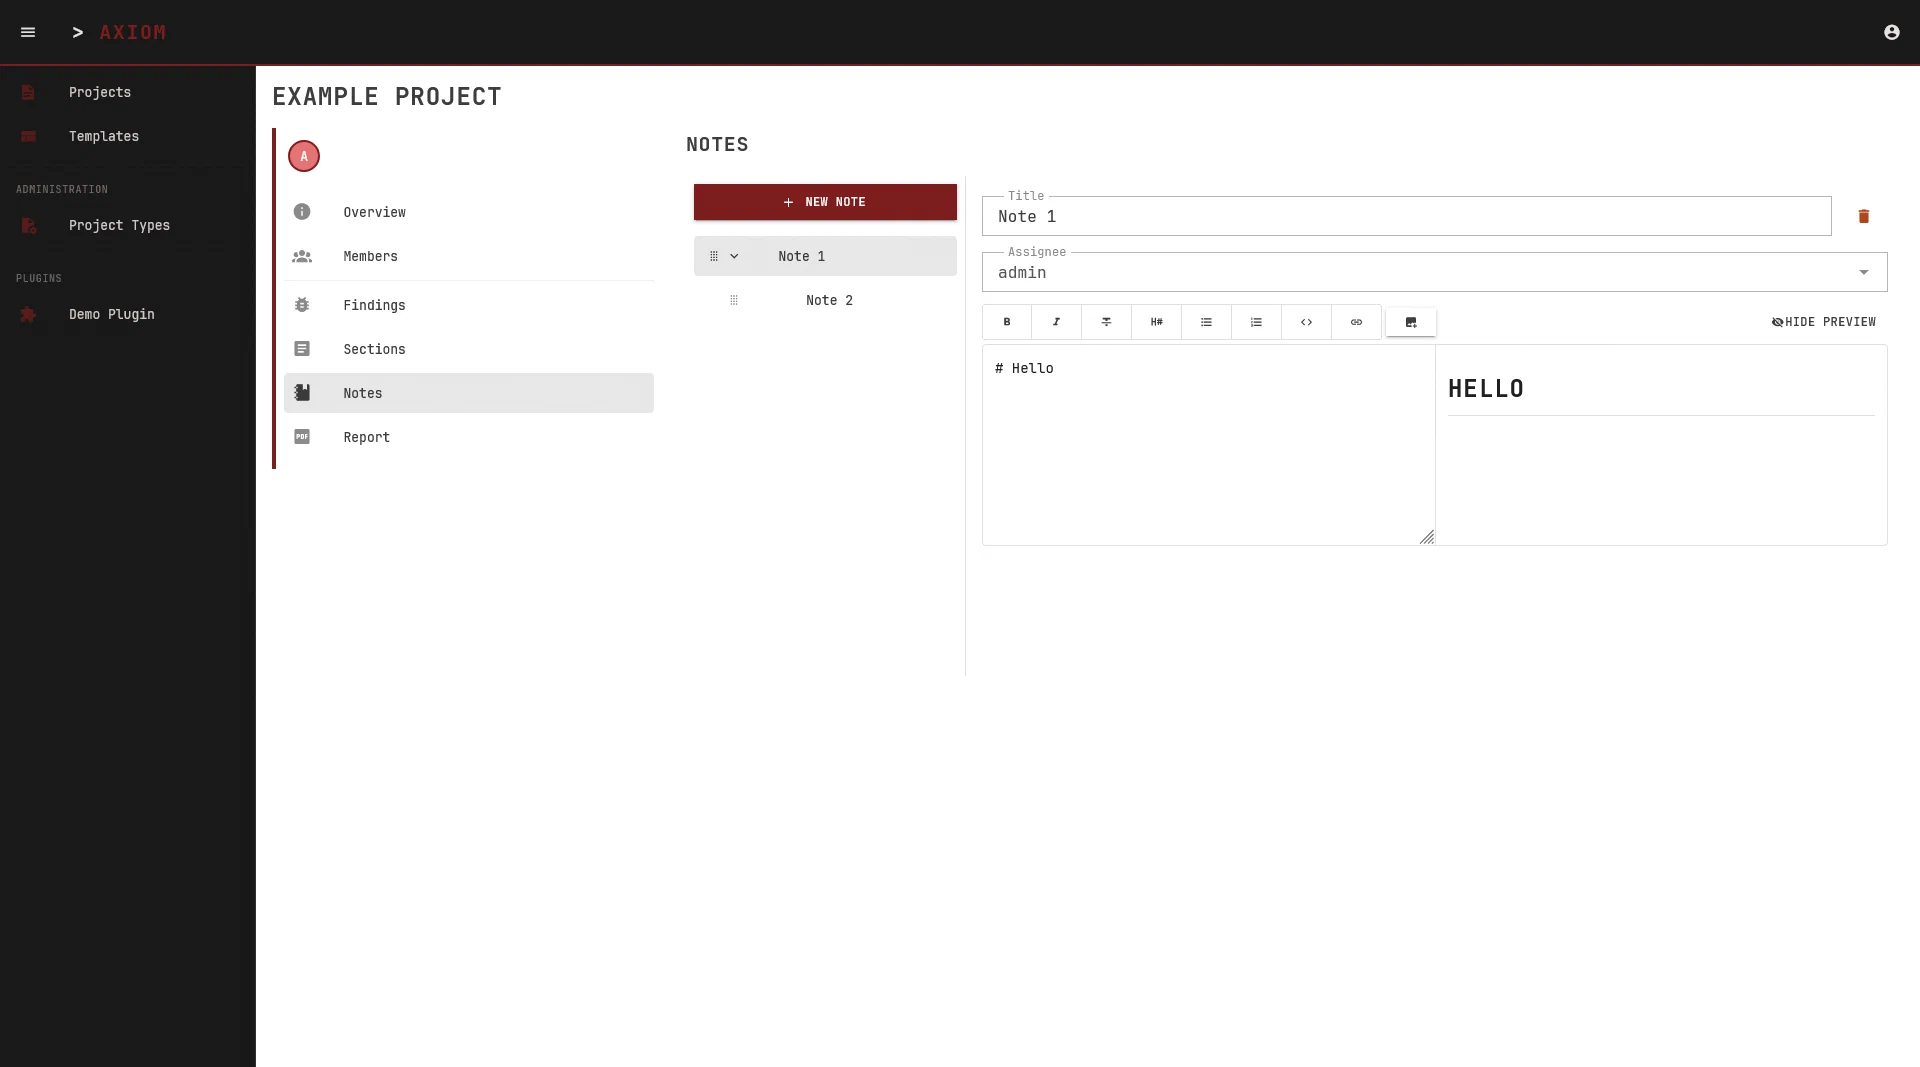
Collaborative project notes
Capture evidence and working context in a split Markdown editing workspace.
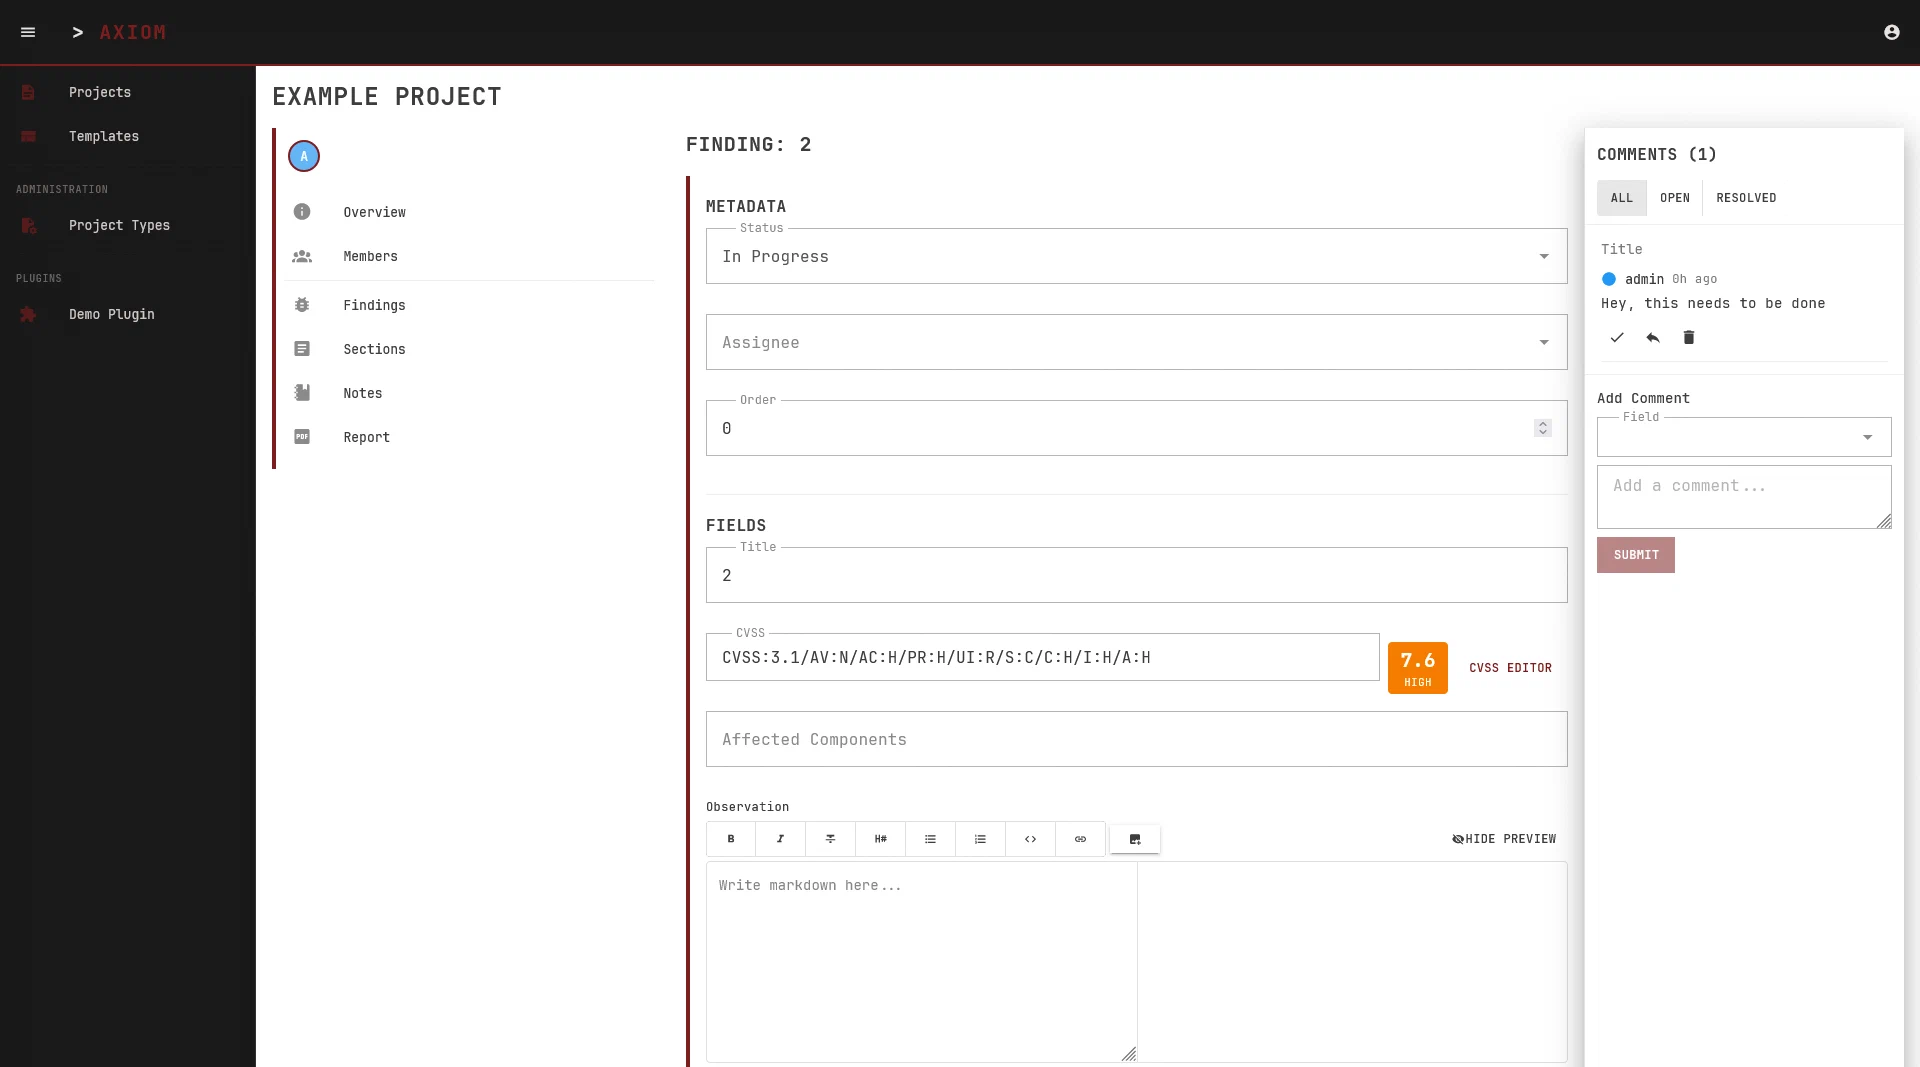
Field-level comments
Leave review comments on the exact field they refer to.
Features
Professional pentest reporting with a terminal-noir aesthetic.
PDF report generation
WeasyPrint-powered output with cover pages, automatic table of contents, severity-coloured finding cards, and full MonoBlood styling.
Real-time collaboration
Several pentesters edit the same project at once — Yjs-powered conflict-free editing with live cursor presence.
Finding management
CVSS 3.1 and 4.0 scoring, severity classification, and structured fields for observation, impact, and recommendation.
Custom project types
Define report sections, finding fields, HTML templates, and CSS per engagement type, then reuse them across teams.
Scanner import
Bring findings in from Burp Suite, Nessus, Nmap, and ZAP. The importer registry is extensible through plugins.
Plugin system
Extend AXIOM with Django app plugins: API endpoints, template tags, signal handlers, importers, and frontend pages.
Report template
Start from a complete A4 report design instead of a blank page. Drop it into a project type and adapt it to your house style.
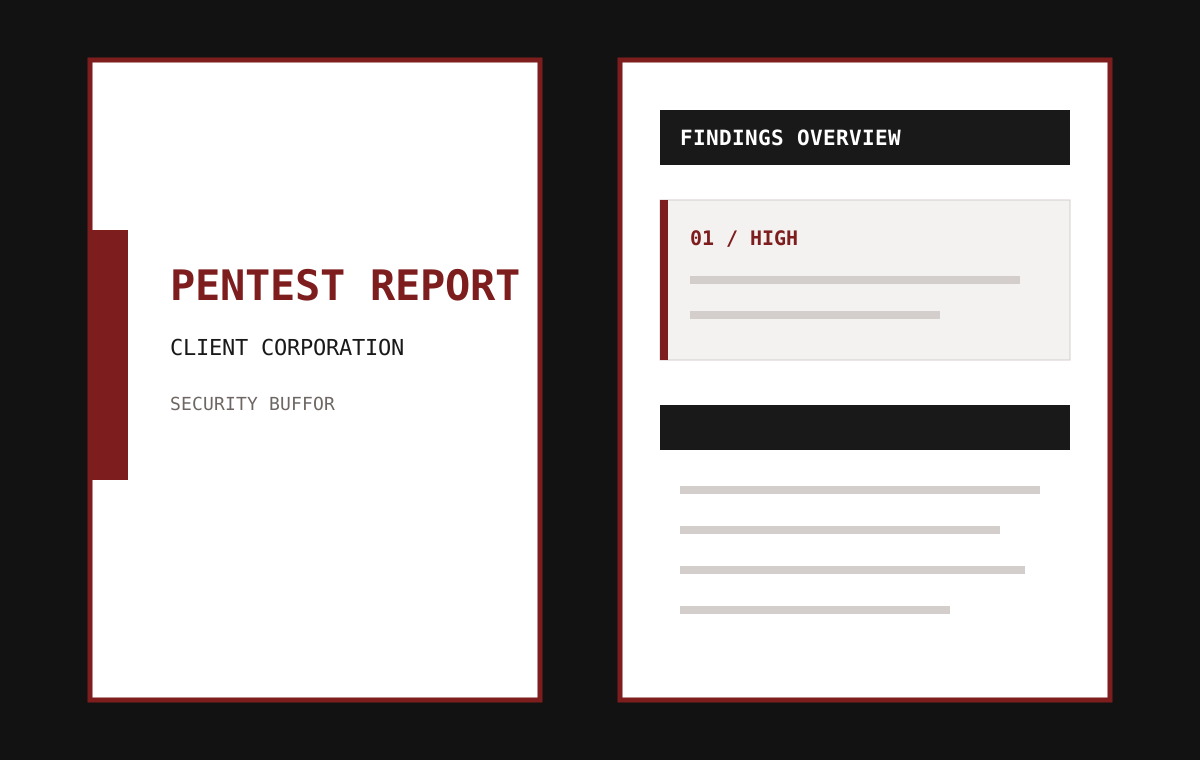
Complete report design
MonoBlood Pentest Report
A complete A4 security-assessment report foundation with cover, table of contents, findings, severity system, tables, and print styling.
What's inside
- Cover page
- Table of contents
- Finding cards
- Severity system
- Data tables
- Code blocks
- Lists & markers
- Typography
Severity scale
- Critical
- High
- Medium
- Low
- Info
Plugins
AXIOM plugins are regular Django apps. Each one can add its own endpoints, importers, report helpers, and pages to the workspace.
Extension points
- API endpoint
- Add routes under /api/plugins/
- Template tags
- Custom tags and filters for reports
- Importer
- Turn any file format into findings
- Signals
- React to project and finding events
- Frontend
- Embed a page in the AXIOM sidebar
Get in touch
See AXIOM on a real engagement.
AXIOM is not public. Reach out for a walkthrough or to hear when it becomes available.